

Qualys TotalCloud 2.29.0 Release Updates

The Qualys TotalCloud 2.29.0 version introduces new capabilities, features, and updates. This release brings very exciting updates that would help simplify your cloud security operations. The release is expected to be available by end of November 2026.
CSPM Enhancements
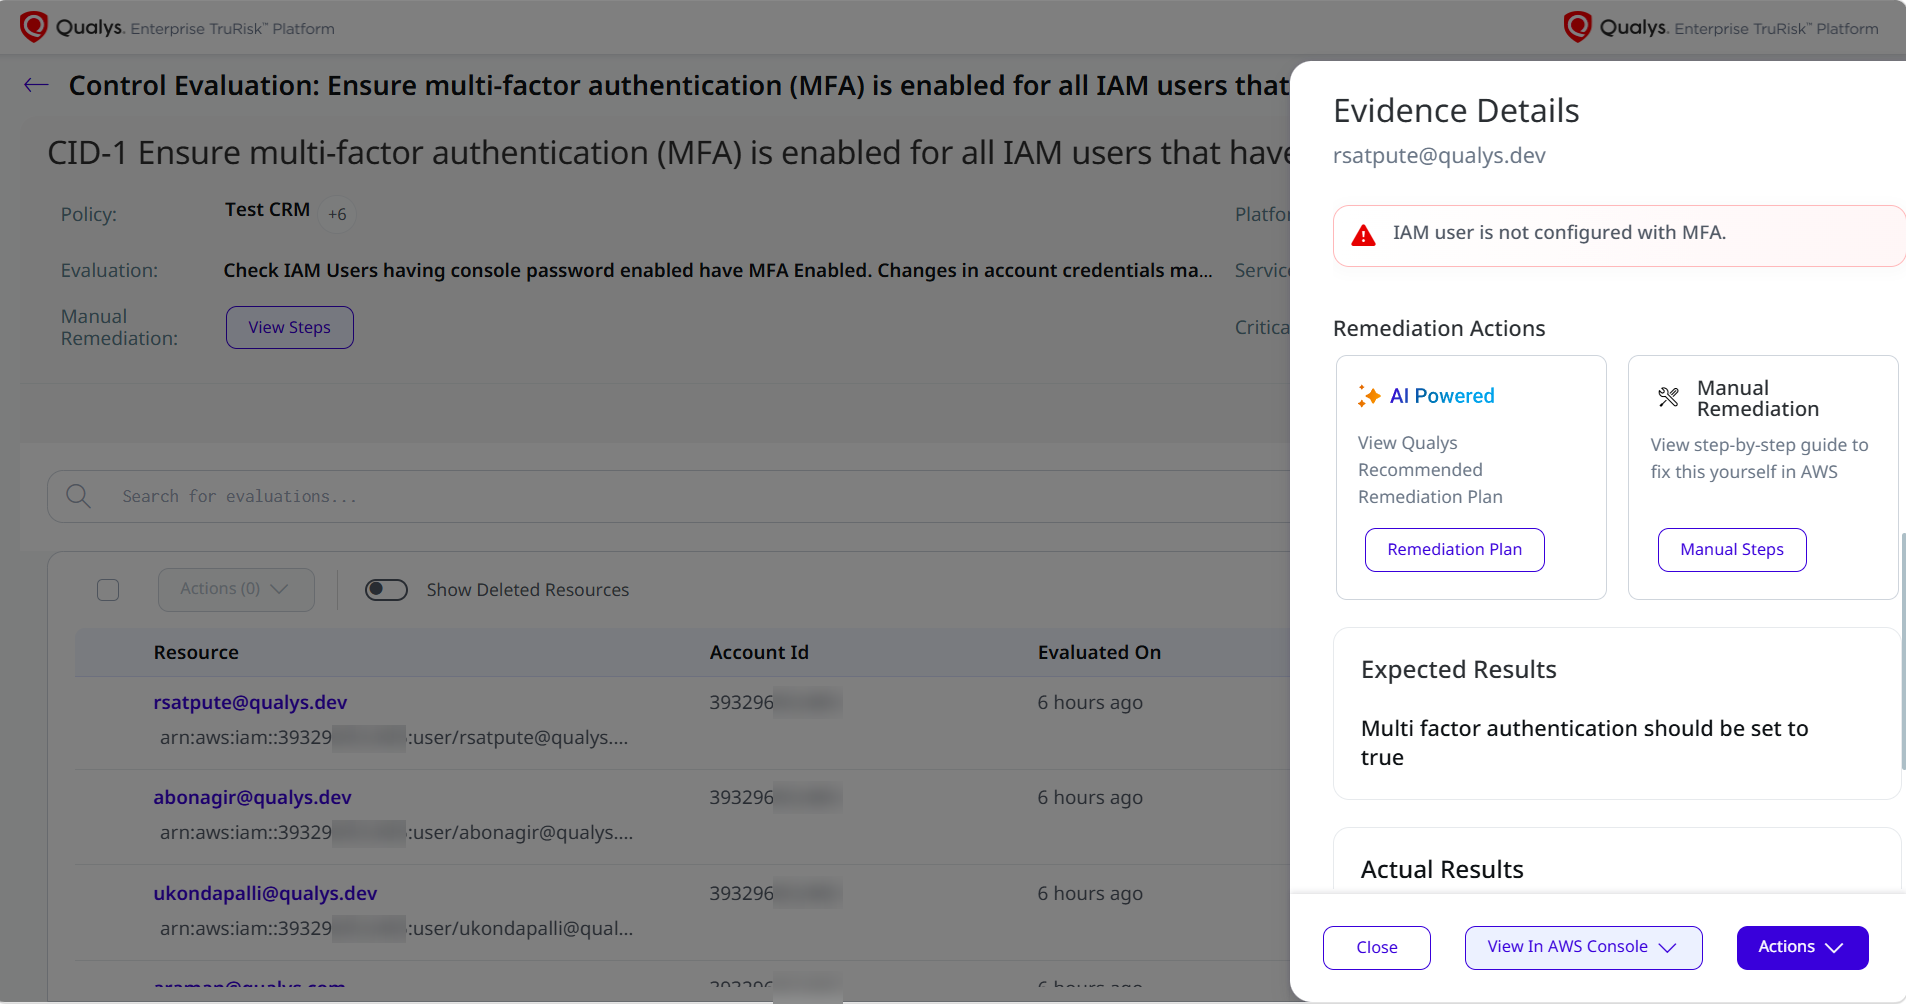
AI-Powered Cloud Remediation Assistant
Detecting a misconfiguration has never been the hard part; closing it is. Qualys TotalCloud now introduces the Cloud Remediation Assistant which turns a posture finding into a ready-to-run remediation plan, generated in the format your team already works in like Terraform, CloudFormation, Bicep, Python, CLI across AWS, Azure, GCP and OCI. Each plan is generated against the specific control and resource, so engineers start with working code they can review and ship, instead of translating a remediation paragraph into something their pipeline will accept.
Key Benefits:
- Remediation keeps pace with detection: The work between “we found it” and “we fixed it” collapses from research and scripting into review and approval, hence keeping pace with remediations.
- Fixes with Code: Plans generated as Terraform, CloudFormation or Bicep offers the code that fixes the misconfigurations, helping you remediate the misconfigured resource without wasting time on writing code or creating remediation plans.
- No new tooling and no new process: Remediation arrives in languages your pipelines, reviews, and change controls already handle, so adopting it doesn’t require a parallel workflow or a new set of permissions in production.
Multi-Cloud Posture View
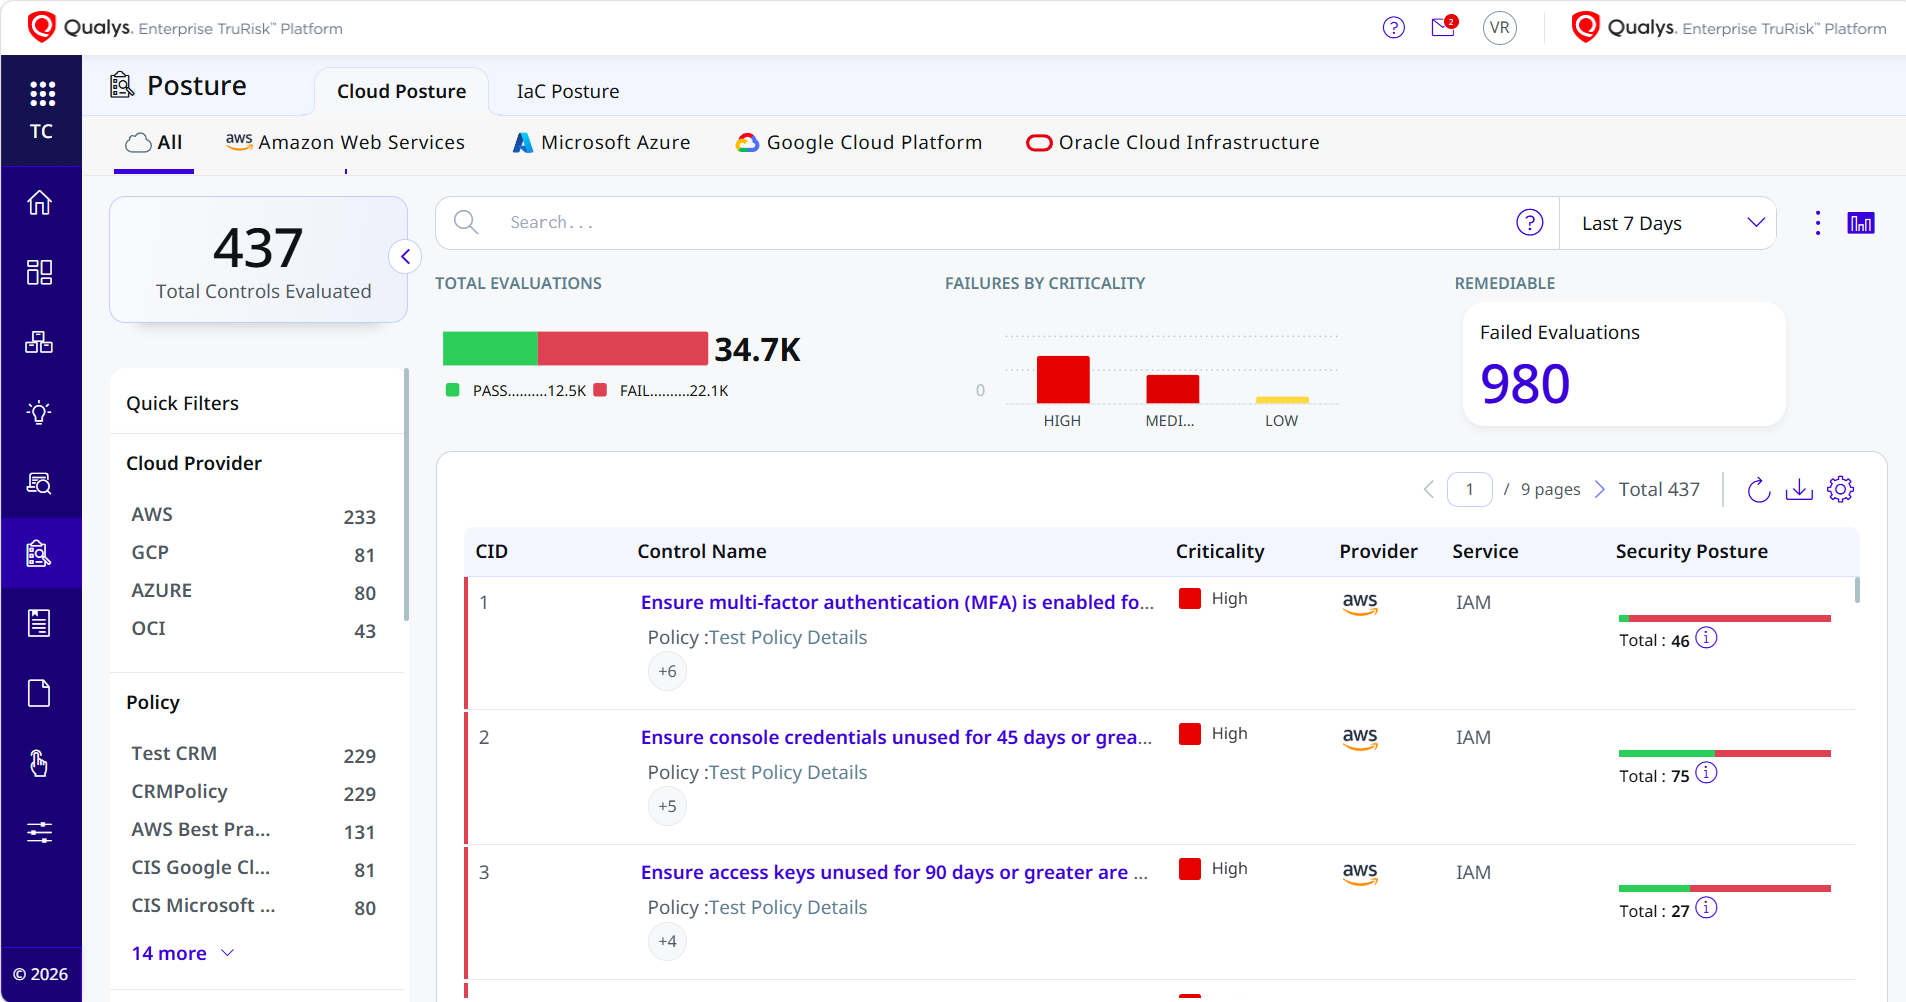
Qualys TotalCloud now presents compliance posture across AWS, Azure, GCP, and OCI in a single view, no cloud selector, no other exports to reconcile before anyone can answer how the overall compliance looks. The Posture Overview brings evaluation and failure statistics, severity breakdowns, along with the accounts, subscriptions, and projects carrying the most risk into one place. The overview page on inventory shows additional global posture statistics.
The All tab lists every evaluation across every cloud, searchable with QQL across control name, CID, resource type, service, and account, with quick filters for account, criticality, policy, service, mandate, and policy compliance scores.
Key Benefits
- From posture to ownership in one path: Filters for top accounts, subscriptions, and projects by findings, with drill-through from any statistic into the underlying evaluations, turning a compliance score into a routable list of work for a named team.
- Single compliance view across the whole estate: Find total evaluations across all clouds in one place, helping you plan the remediations and improve the posture across clouds.
Multi-Cloud Dashboards
Qualys TotalCloud introduces Multi-Cloud Dashboards, providing a unified view of cloud security posture and inventory across supported cloud environments. These dashboards and widgets help security teams consolidate key insights, monitor their cloud environments, and gain a clearer understanding of their overall security posture from a centralized view.
Key Benefits
- Simplified Security Monitoring: Track key metrics and security insights without switching between individual cloud environments.
- Improved Executive Reporting: Present cloud security posture and inventory information through dashboards that support security reviews and stakeholder reporting.
Richer, More Configurable Assessment Reports
Qualys TotalCloud continues to enhance its CSPM reporting capabilities, providing greater flexibility and customization when generating reports. With this release, customers can select from an expanded set of attributes when creating CSPM reports, including Control Name, Remediation Steps, Specification, Rationale, Account Alias, Organization Name, and various tag types such as Connector Tags, Account Tags, Resource Tags, and Dynamic Tags.
These additional attributes enable customers to tailor downloadable and scheduled CSPM reports to their specific operational, security, and compliance requirements, making it easier to analyze findings, identify remediation actions, and organize results across cloud environments.
Key Benefits
- Flexible Report Customization: Select relevant attributes to create reports tailored to specific needs.
- Improved Remediation Guidance: Include control details, rationale, and remediation steps to support faster resolution.
Audit Logging for Reports, Alert Rules, and Exceptions
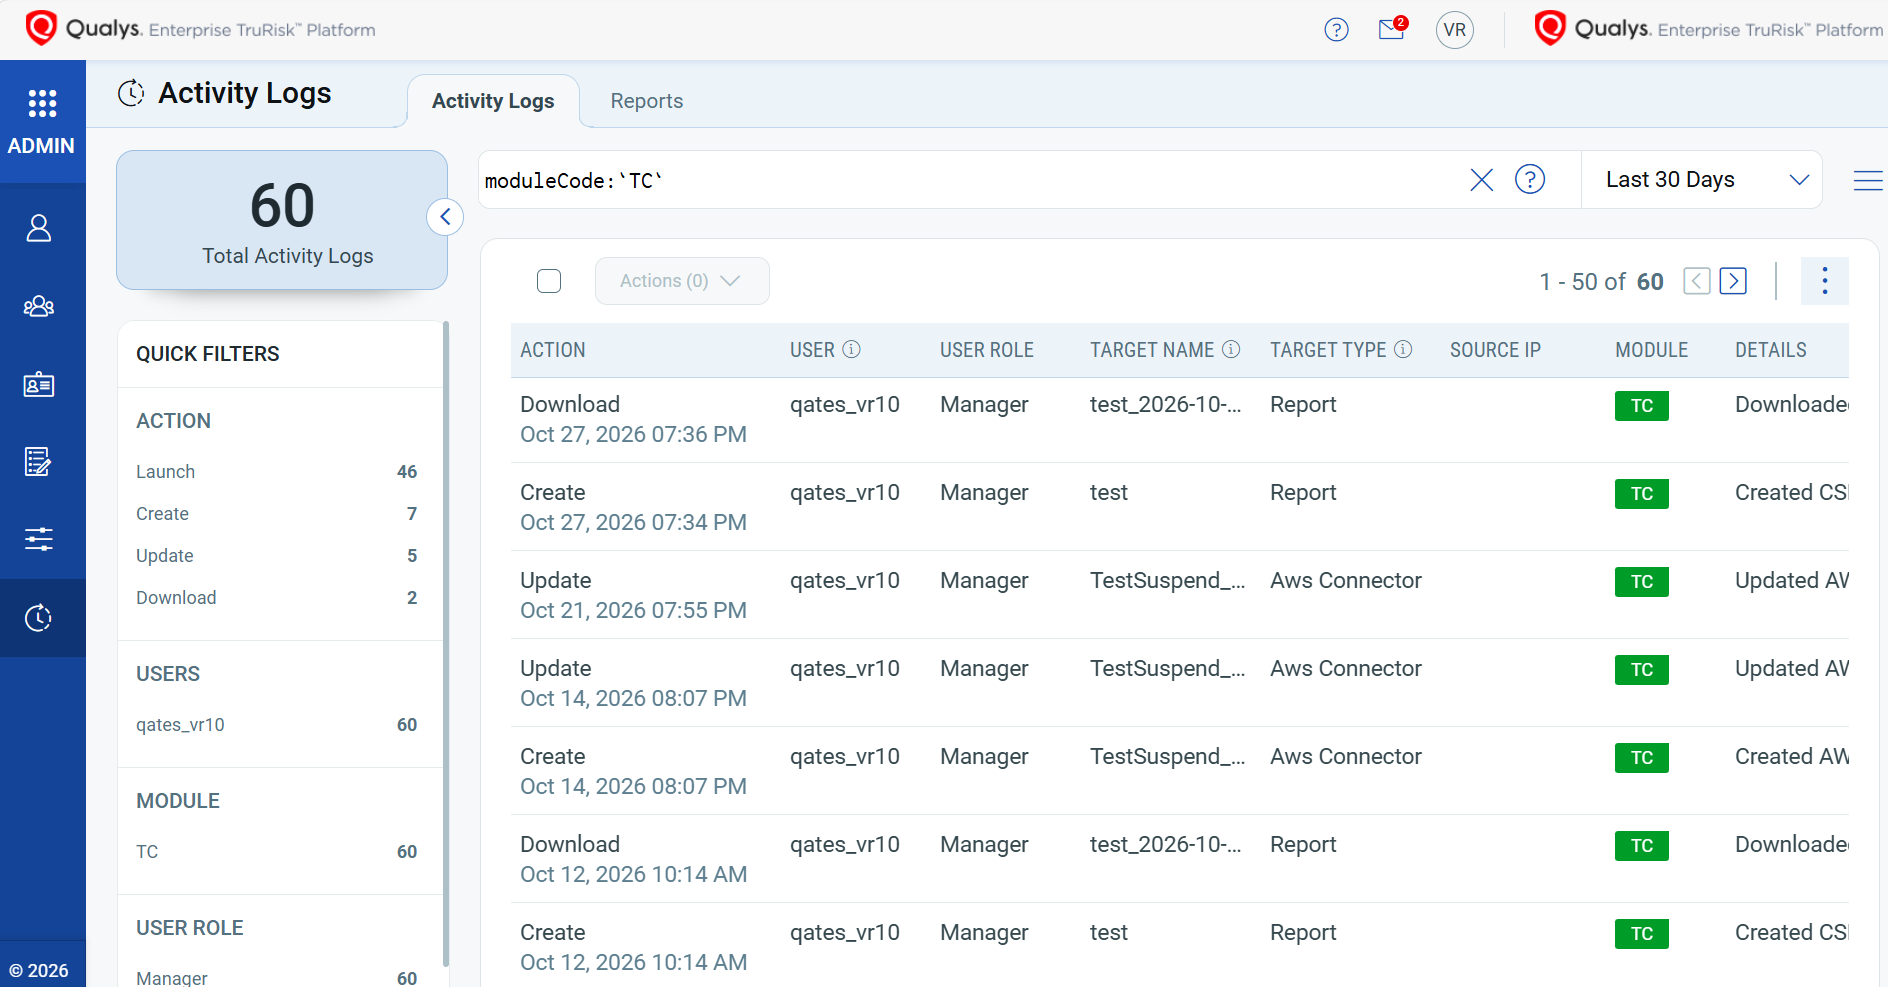
Qualys TotalCloud enhances auditability and operational transparency by capturing key actions related to CSPM reports, alert rules, and exceptions across AWS, Azure, GCP, and OCI. Audit logs record activities such as creating or removing exceptions, enabling or disabling alert rules, and scheduling, running, or downloading reports. Each event captures details such as the user, role, timestamp, and source of the action, whether performed through the TotalCloud console or public API.
Customers can search audit logs using QQL and export logs for external retention and further analysis.
Key Benefits
- Monitor and Track Critical Configuration Changes: By recording these activities with user, role, timestamp, and source details, TotalCloud helps teams detect changes that may affect security monitoring or reporting continuity.
- Simplify Investigation and Compliance Reviews: Search, analyze, and export audit events to support investigations, internal reviews, and compliance evidence collection.
CWPP Enhancements
OCI snapshot scan
Qualys TotalCloud is now extending snapshot-based scan capabilities to include OCI Cloud, providing comprehensive coverage for both online and offline VMs, reducing operational overhead and avoiding disruptions to running workloads.
By integrating this advanced capability, Qualys simplifies the management of security assessments across your OCI environment, offering seamless and automated vulnerability detection without manual intervention.
Key Benefits:
- Agentless and Non-Intrusive: Snapshot scanning approach minimizes operational overhead and ensures that scanning activities do not interfere with the performance of live systems.
- Reduces agent management costs and complexity: Agent rollouts stall on change windows, workload owners, and legacy images. Snapshot scanning gets your OCI virtual machines assessed without touching them.
Inventory Visibility Enhancements
Inventory Extract from “All” tab.
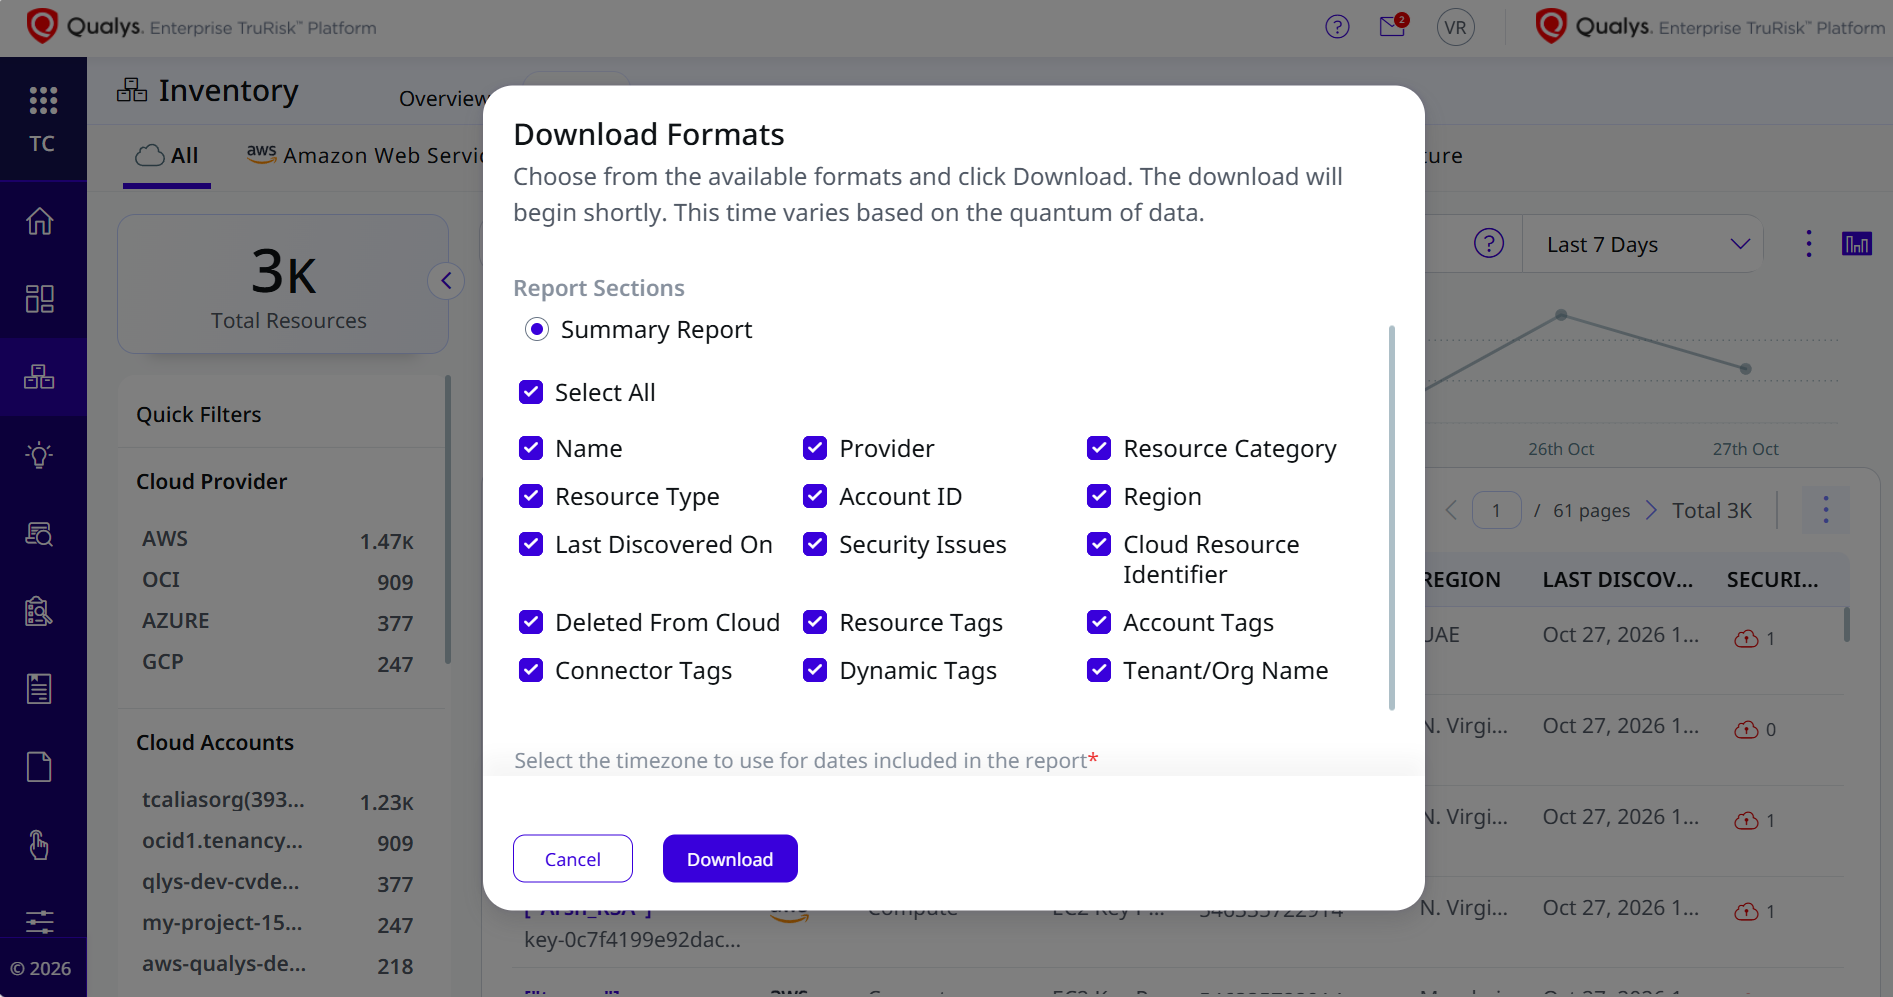
Qualys TotalCloud enables customers to export their multi-cloud resource inventory directly from the All tab under Inventory as a CSV file, with the flexibility to select the attributes they need. The export consolidates resource inventory across AWS, Azure, GCP, and OCI into a single file, making it easier to analyze, report on, and integrate inventory data into downstream workflows.
This release expands the available export attributes to include Cloud Resource Identifier, Last Discovered Date, Open Security Issues, Tenant/Organization Name, resource deletion status (Deleted from Cloud), and comprehensive tagging details across Resource Tags, Account Tags, Connector Tags, and Dynamic Tags.
Note: This option downloads up to 10,000 records. To extract larger volumes, use the Reporting section, which supports high-volume report generation per cloud provider.
Expanded Inventory Coverage.
| Feature | What’s Updated |
| Expanded GCP Inventory Coverage | Qualys TotalCloud now extends detailed inventory support for the following critical GCP Resource types. Vertex AI Endpoint Colab Runtime Templates Workbench Instances BigQuery Table API Keys All organized across dedicated tabs for tags, summary details, controls evaluated, and resource metadata. |
| Expanded OCI Inventory Coverage | Qualys TotalCloud now extends detailed inventory support for the following critical OCI AI Resource types. AI Document Model AI Document Project AI Language Model AI Language Project AI Speech Customization AI Speech Transcription Job AI Vision Model AI Vision Project Data Science Project Data Science Model Data Science Model Deployment Data Science Model Group |
CSPM Control Enhancements
New Controls Introduced
Qualys continuously monitors new security controls across cloud platforms. In this release, approximately 9 new Azure security controls are introduced.
Additional Permissions for Controls
We have introduced many new controls (as mentioned in the above section) with this release, and the required granular permissions for those control evaluations are listed below.
| Cloud Provider | Permissions |
| Azure | Microsoft.DBforPostgreSQL/flexibleServers/privateEndpointConnections/read Microsoft.Sql/managedInstances/vulnerabilityAssessments/read Microsoft.ApiManagement/service/subscriptions/read Microsoft.ApiManagement/service/backends/read Microsoft.Authorization/roleDefinitions/read Microsoft.KeyVault/managedHSMs/read Microsoft.ResourceGraph/resources/read Microsoft.RecoveryServices/vaults/backupFabrics/protectionContainers/protectedItems/read |
Additional Permissions for Inventory
We have introduced support for many new cloud services with the TotalCloud 2.28.0 release, and the required granular permissions for the resource inventory are listed below.
| Cloud Provider | Permissions |
| GCP | aiplatform.endpoints.list aiplatform.notebookRuntimeTemplates.list notebooks.instances.list bigquery.datasets.get bigquery.tables.list bigquery.tables.get apikeys.keys.list |
Resources
- TotalCloud™ – The Risk-minded CNAPP. Learn more about TotalCloud CNAPP.
- Online Help for TotalCloud, Connectors, TotalCloud API User Guide
- How-to Training Videos
If you have questions, please contact your TAM or Qualys Technical Support.