

Qualys TotalCloud 2.27.0 Release Updates

The Qualys TotalCloud 2.27.0 version introduces new capabilities, features, and updates. This release brings very exciting updates that would help simplify your cloud security operations. The release is expected to be available by the end of August 2026.
CWP: Cloud Perimeter Scan for OCI Cloud
Qualys TotalCloud now extends Cloud Perimeter Scan support to Oracle Cloud Infrastructure (OCI), automatically discovering internet-facing compute assets with public IP addresses and onboarding them for VMDR vulnerability assessment, no manual intervention required.
This brings OCI to full feature parity with AWS, Azure, and GCP, delivering continuous visibility into your external attack surface across all major cloud platforms.
Key Benefits:
- Automated internet-facing asset discovery: Public-IP compute assets in OCI are continuously discovered and automatically activated for VMDR scanning during connector onboarding.
- Reduced external attack surface exposure: Vulnerabilities in publicly accessible OCI workloads are identified and prioritized before they can be exploited, with no manual onboarding overhead.
CSPM: Real-Time Inventory with Azure EventGrid (Delta Sync)
Qualys TotalCloud now extends real-time inventory updates for Azure Cloud resources through native Azure EventGrid integration. Rather than waiting for scheduled sync cycles, TotalCloud instantly responds to infrastructure changes, triggering inventory updates the moment resources are created, modified, or deleted. A full sync continues on the recommended 48-hour cycle, with full backward compatibility for existing connector sync processes.
Key Benefits:
- Immediate cleanup for deleted resources: Assets deleted from Azure are instantly marked as deletedFromCloud upon delete events, before the next regular sync cycle.
- Always-current posture: Compliance status updates automatically the moment a resource is remediated, no waiting for the next scheduled evaluation.
Connector Enhancements
Qualys continuously evolves its Connector experience to ensure teams always have access to the latest capabilities and can use them effectively, with less noise, more flexibility, and faster access to the information that matters.
Connector Errors to Logs
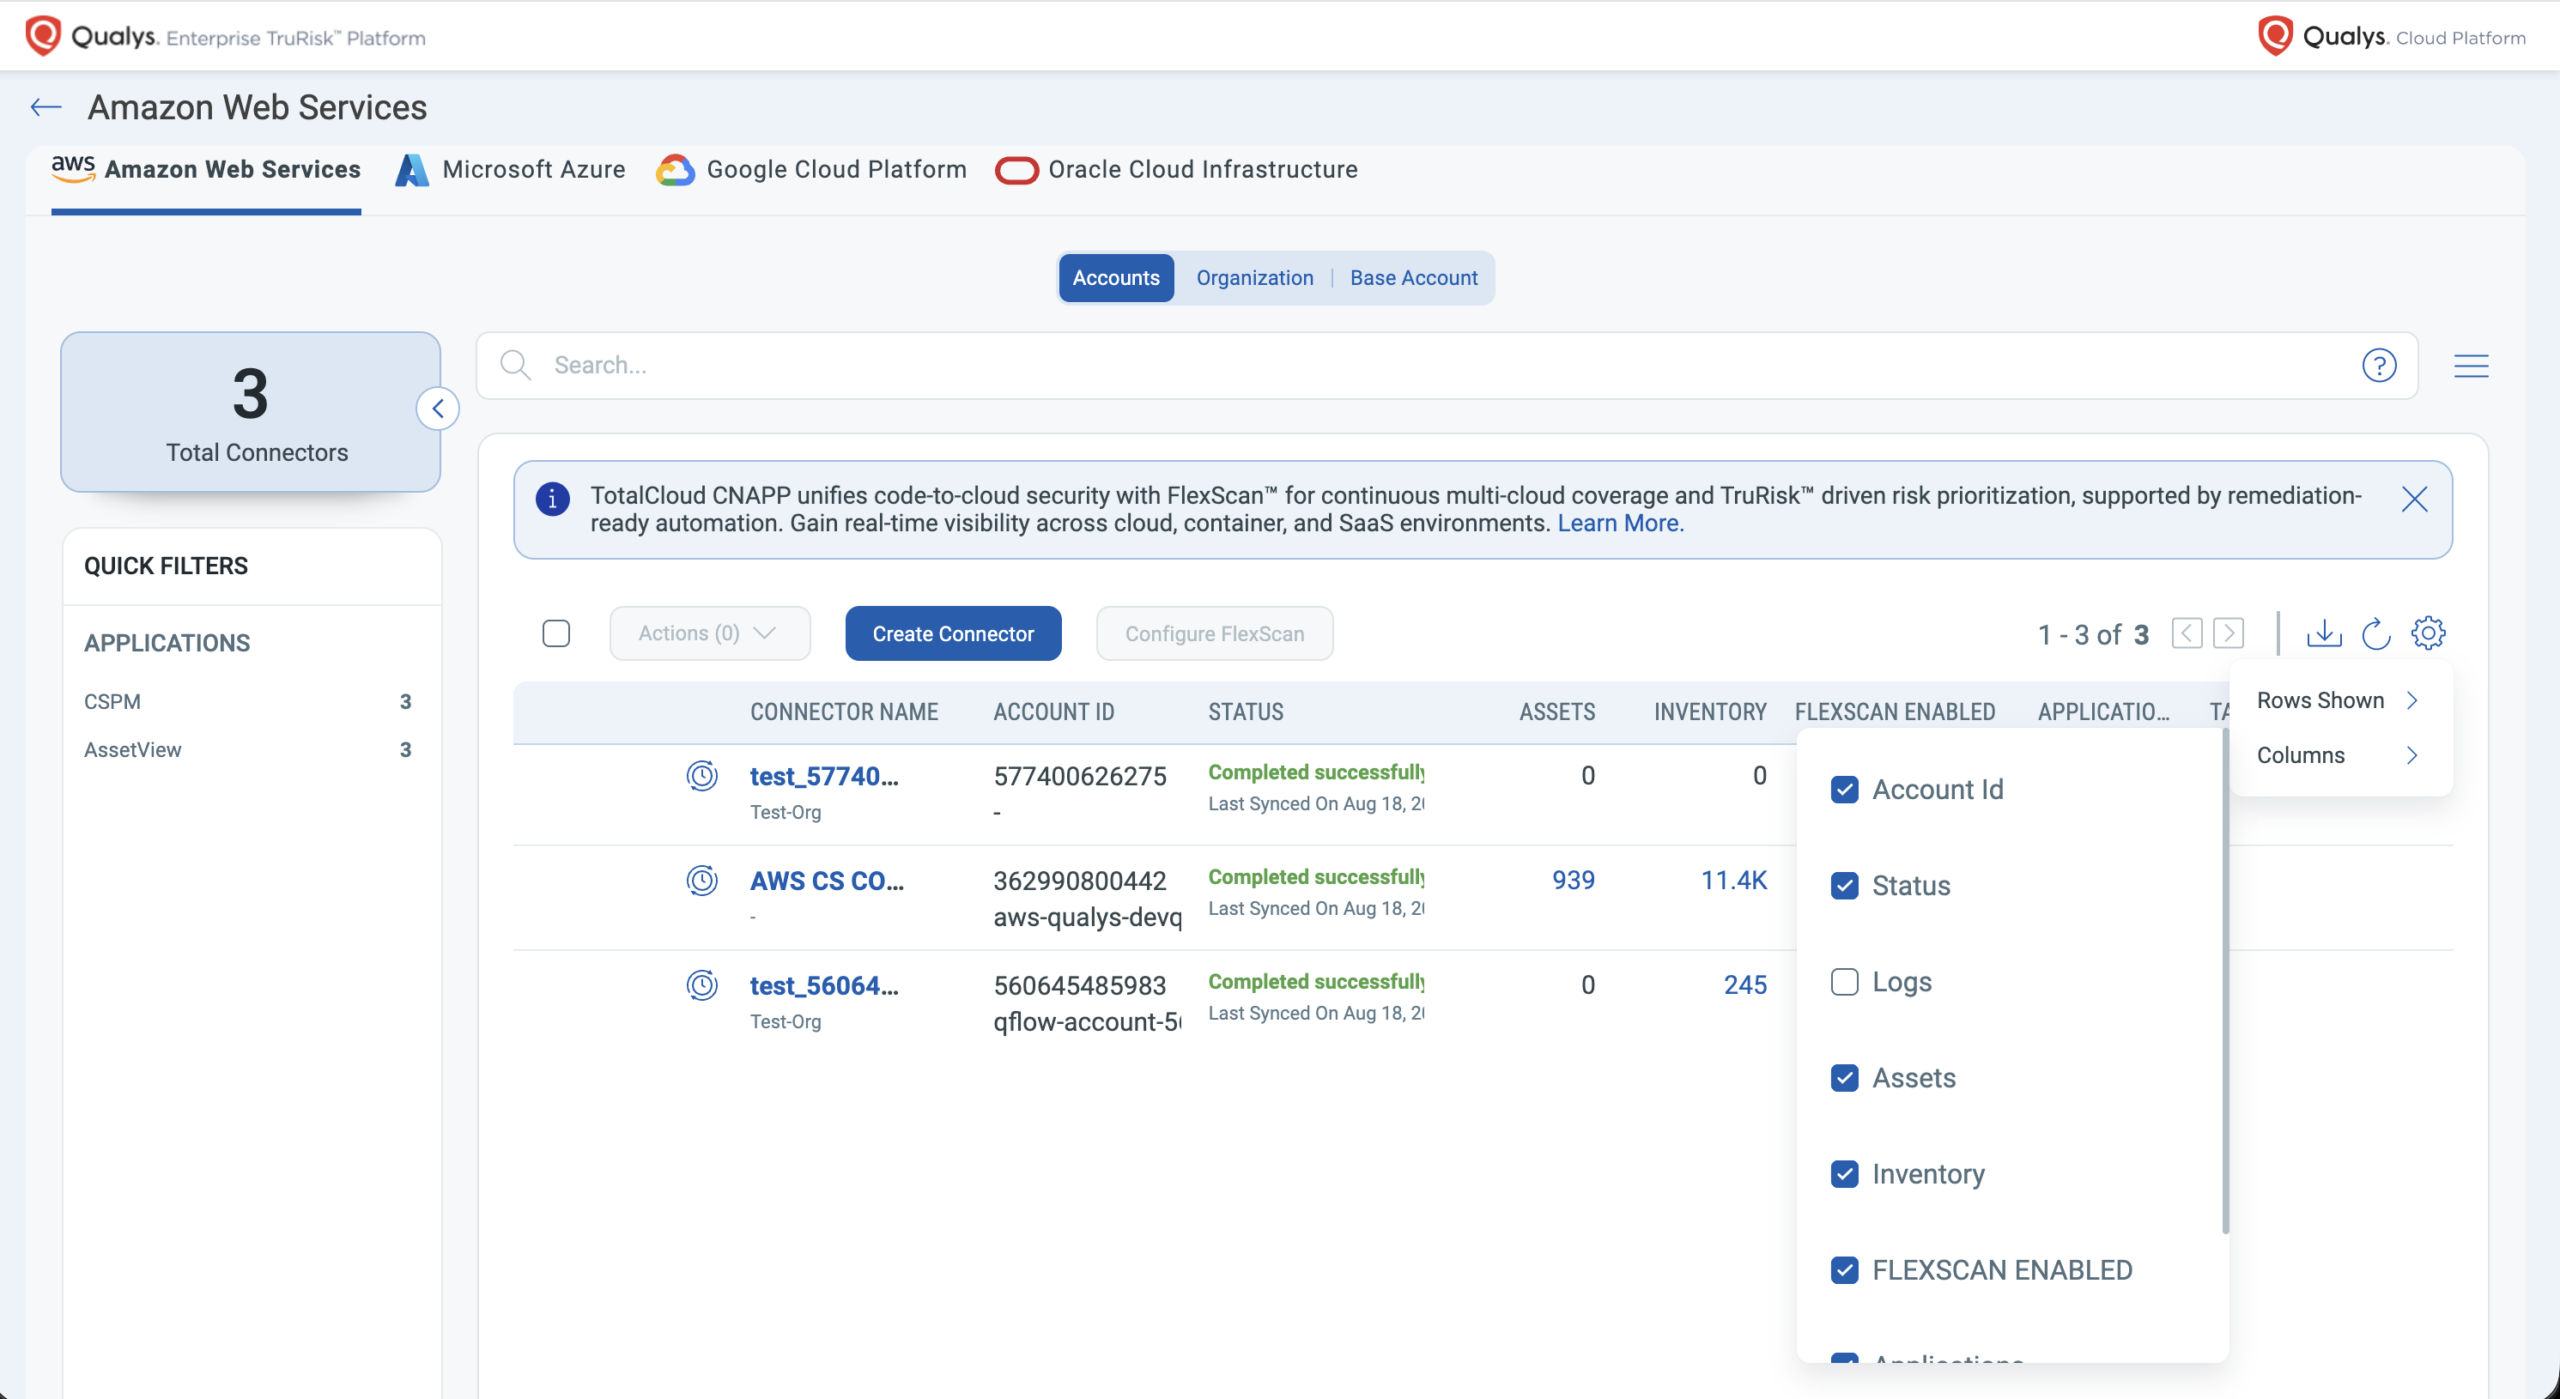
Qualys TotalCloud has renamed Connector Errors to Logs, better reflecting the full scope of activity captured beyond just errors. To reduce visual noise on the Connector listing page, the Logs column is now hidden by default, keeping the interface clean and focused. Users can reveal it at any time with a single click when a deeper diagnostic context is needed.
CSPM Connector Status
Qualys TotalCloud is simplifying connector health monitoring by removing the Status column from the CSPM Connectors tab under TotalCloud > Configure > CSPM Connectors. This column will be deprecated in this release to eliminate confusion between redundant status indicators and the more comprehensive, accurate information available in Connector Logs.
For the most reliable and detailed view of connector health and issues, we recommend using the Connector Logs section going forward.
Note: Removing the Status column from CSPM Connectors does not affect connector functionality or data collection. This is a UI cleanup to consolidate connector health monitoring into a single, authoritative location.
Wildcard Support for Tag-Based Connector Search
Qualys TotalCloud now supports wildcard-based filtering for connector tag searches, enabling users to find connectors using flexible match patterns – Contains, Starts With, and Ends With. This makes it significantly faster to locate connectors across large environments where tags follow naming conventions or partial patterns, without needing an exact match.
Note: This is currently available with case-sensitive searches.
Key Benefits:
- Flexible, pattern-based search: Filter connectors by partial tag values using Contains, Starts With, or Ends With, no need for exact tag names to find what you’re looking for.
- Faster connector management at scale: Quickly locate and manage groups of connectors that share tag naming conventions across large, multi-account cloud environments.
Risk Prioritization
Qualys TotalCloud brings attack path visibility directly into the inventory and posture workflow, enabling security teams to focus remediation where it matters most, not where it’s easiest.
Field hasAttackPath for Compute Assets in v2 Resource API
The v2 Resource API for compute assets now includes the hasAttackPath field as a supported filter, enabling teams to programmatically export only the inventory records with active attack paths identified.
This brings attack path risk intelligence into automated pipelines, dashboards, and CMDB workflows, ensuring downstream integrations surface the assets that truly matter without manual filtering or secondary lookups.
Key Benefits:
- Export a targeted, attack-path-filtered compute inventory via API, no manual post-processing or cross-referencing required.
- Feed confirmed high-risk assets directly into ticketing, SIEM, or remediation workflows for faster, automated response at scale.
Inventory Visibility Enhancements
Qualys TotalCloud continuously refines the inventory experience, expanding cloud coverage, improving how data is surfaced, and ensuring every team can access, filter, and export the information they need, faster and with less friction.
| Feature | What’s Updated |
| Commonly Used Services in Resource Type Filter | Based on customer feedback, the most frequently accessed resource types now appear at the top of the resource type filter, making it faster to navigate to the services you use most without scrolling through the full list. This small but impactful change reduces the clicks needed during daily inventory reviews and accelerates triage workflows for security and cloud operations teams. |
| Expanded REST API Coverage for Inventory Export | REST API coverage now extends to all resource types, enabling teams to programmatically fetch complete inventory exports from the Qualys Platform, powering automation workflows and integrations without manual intervention. This ensures no resource type is left out of automated pipelines, dashboards, or CMDB sync workflows, giving teams a truly complete and accurate cloud inventory through APIs. |
| Time-Based Filtering for Global Inventory View | The multi-cloud global inventory view now supports time-based filtering — Last 24 Hours, Last 7 Days, and Last 30 Days, giving teams the ability to focus on recently discovered or changed resources across all cloud deployments at a glance. This makes it significantly easier to track infrastructure changes over time, spot newly introduced resources, and investigate recent activity without manually adjusting filters on every session. |
| MultiCloud Inventory Overview, Expanded Context and CSV Export | The MultiCloud Inventory Overview now surfaces resources that are not yet evaluated alongside assessed ones, giving a complete and unfiltered picture of your cloud estate across AWS, Azure, GCP, and OCI. Teams can also export the full inventory view in CSV format for offline analysis, reporting, and compliance documentation — bridging the gap between the TotalCloud UI and external reporting or ticketing workflows. |
Expanded Cloud Inventory Coverage Across AWS, Azure, GCP, and OCI
Qualys TotalCloud continues to broaden its cloud inventory coverage across all four major cloud platforms, AWS, Azure, GCP, and OCI, adding support for new resource types based on direct customer requests. Each release broadens the range of discoverable resources, ensuring that security teams have a more complete and accurate foundation for posture assessment, compliance reporting, and risk analysis.
Below is the list of the resources that are introduced, and additional granular permission requirements
| Provider | Newly added resources |
| AWS | AWS SSM Document, AWS CodeBuild Project, ACM Certificate, Amazon DynamoDB Table, Amazon EventBridge Rule, Amazon Network Firewall, Amazon Athena Workgroup, Amazon Network Firewall Policy, AWS IAM Server Certificate, CloudTrail Trail |
| Azure | Logic App Workflow, Security Center Settings, Streaming Jobs (Azure Stream Analytics Jobs) API Management APIs Workspace, Activity Log Alert, Bastion Host, CDN endpoint, CDN profile, Backup Vault Policy (Azure Data Protection Backup Policies), Backup Vault (Azure Data Protection Backup Vaults), Front Door, Key Vault Managed Hsms, Diagnostic Settings, Azure Policy Assignment, Recovery Service Vault, Recovery Service Vault Backup Policy, Azure SignalR Service, Web PubSub, Subscriptions |
| GCP | AI Agents Registry, Generative AI Agents |
| OCI | OCI Subnets, Generative AI Agents Generative AI Agents Endpoints |
CSPM Enhancements
Simplified Time Filter by deprecating “Today”
The ambiguous “Today” option has been removed from time filters across TotalCloud and replaced with clear, consistent options: Last 24 Hours, Last 7 Days, and Last 30 Days, now defaulted to Last 7 Days for broader visibility out of the box.
This preference applies uniformly across Posture, Inventory, Insights, Investigation, and Dashboard views, and every user can adjust it to suit their own workflow at any time.
Note: The deprecation of the “Today” selection is a non-impacting change.
Key Benefits:
- Clearer time context: Removing the ambiguous filter eliminates confusion and ensures consistent, comparable views across all CSPM surfaces.
- Personalized visibility: Each user can set and save their preferred time range, which is applied consistently across Posture, Inventory, Insights, Investigation, and Dashboard in a single setting.
Richer Alert Notifications with Custom Fields
TotalCloud Alerts now support custom fields, enabling teams to compose tailored notification messages that include the exact resource context recipients need to act.
This moves alert notifications from generic triggers to precise, actionable signals that help the right people prioritize and respond faster without additional investigation.
Key Benefits:
- Context-rich alerts: Add custom fields to notification messages so recipients immediately understand which resource is affected, why it matters, and what action to take.
- Faster prioritization: Richer alert content reduces the back-and-forth needed to identify the impacted resource, cutting time from alert to remediation.
Policy and Posture Management
Qualys TotalCloud continues to strengthen its CSPM governance capabilities, from granular access control and audit transparency to improved navigation, policy creation, and consistent compliance reporting. These updates are designed to give security teams greater control, clearer visibility, and a more efficient workflow across policy and posture management.
| Feature | What’s Updated |
| RBAC for CSPM Policy and Control Management | TotalCloud now introduces role-based access control specifically for policy and control management, replacing broad permissions with action-level controls. Admins can precisely define who can create, edit, delete, or only view policies and controls, enforcing least-privilege governance across the team without impacting other TotalCloud permissions. |
| Scope Based Access for CSPM Policy, Control, and Resource Management | Scope-based access is now extended across policy, control, and resource management, ensuring sub-users see and act only on the resources and policies within their assigned connector tag scope. Users can also choose how they want to enforce visibility on posture tab, whether based on connector or asset level scope or based on policy level scope. This brings consistent, tag-driven access enforcement across the full CSPM workflow, from posture findings to policy governance. |
| Create Policies from Existing Policies | Security teams can now create new policies by cloning existing ones, preserving control mappings, tags, and configurations as a starting point. This eliminates repetitive setup, accelerates policy rollout for new environments, and ensures new policies inherit the structure and standards already established by your team. |
| Audit Log Support for Policy and Controls | All policy/controls additions, modifications, and removals on policies and controls are now captured in audit logs, providing a complete, timestamped record of who applied or changed scope and when. This enhances governance accountability and gives compliance teams a reliable trail for policy change reviews and audit submissions. |
| Direct Resource Navigation from Azure Posture Findings | Azure posture evaluation results now include a direct link to the corresponding Azure cloud resource, enabling teams to navigate straight from a misconfiguration finding to the resource in context — without switching consoles or manually searching. This significantly reduces investigation time and accelerates remediation for Azure workloads. |
| Consistent Compliance Scores Across Exports and Dashboards | A previously reported discrepancy between compliance scores shown in dashboard views and those exported in reports has been resolved. Scores are now calculated and presented consistently across all surfaces, ensuring teams, auditors, and stakeholders are always working from the same accurate compliance picture regardless of where they access it. |
| JPQL Function Catalog for Custom Controls | TotalCloud now surfaces a built-in JPQL Function Catalog directly within the custom controls experience, giving security engineers easy access to the full library of available functions when building complex queries. Introduced in TotalCloud 2.26, this enhancement removes the guesswork from writing advanced JPQLs, teams can browse, reference, and apply functions without leaving the control builder, accelerating the creation of sophisticated, accurate custom controls. |
| Clone Existing Custom Controls | Users can now clone existing custom control, both out-of-box and custom, as a starting point for new ones, carrying forward the underlying JPQL query, configurations, and metadata. This eliminates redundant rebuild effort, ensures consistency across similar controls, and significantly speeds up control creation for teams managing large control libraries across multiple policies. |
| Dedicated Policy for AI Service Best Practices Policy | Qualys TotalCloud now introduces a dedicated out-of-box security policy for AI services across AWS, Azure, GCP, and OCI,enabling teams to immediately assess AI and machine learning service configurations against curated best practice controls, without building custom policies from scratch. |
CSPM Control Enhancements
New Controls and Title Updates
Qualys continuously monitors new security controls across cloud platforms. In this release, the following new controls have been added:
- AWS: Approximately 15 new security controls are introduced
- Azure: Approximately 41 new security controls are introduced
- Azure: Approximately 8 new security controls are introduced
We also enhanced existing controls to keep them up-to-date.
| For ongoing updates on control changes, refer to the TotalCloud Release Notes for version 2.27, which will be published soon on the Qualys Product Release Notes page. |
New Control Permissions
We have introduced many new controls (as mentioned in the above section) with the TotalCloud 2.27.0 release, and the required granular permissions for those control evaluations are listed below.
| Cloud Provider | Permissions |
| Azure | Microsoft.Web/sites/Read Microsoft.Web/sites/slots/Read Microsoft.Web/sites/slots/config/Read Microsoft.Storage/storageAccounts/read Microsoft.Storage/storageAccounts/blobServices/read Microsoft.Storage/storageAccounts/fileServices/read Microsoft.Storage/storageAccounts/queueServices/read Microsoft.Storage/storageAccounts/tableServices/read Microsoft.StreamAnalytics/streamingjobs/read Microsoft.Insights/diagnosticSettings/read Microsoft.Compute/virtualMachineScaleSets/read Microsoft.Search/searchServices/read Microsoft.DBforMySQL/flexibleServers/read Microsoft.DBforPostgreSQL/flexibleServers/read Microsoft.ContainerService/managedClusters/read Microsoft.DocumentDB/databaseAccounts/read Microsoft.MachineLearningServices/workspaces/read Microsoft.Sql/managedInstances/read Microsoft.Synapse/workspaces/read Microsoft.Synapse/workspaces/azureADOnlyAuthentications/read Microsoft.Network/virtualNetworkGateways/read Microsoft.DBforPostgreSQL/flexibleServers/configurations/read |
New Inventory Permissions
We have introduced support for many new cloud services with the TotalCloud 2.27.0 release, and the required granular permissions for the resource inventory are listed below.
| Cloud Provider | Permissions |
| AWS | athena:GetWorkGroup, athena:ListWorkGroups, network-firewall:ListFirewallPolicies, network-firewall:DescribeFirewallPolicy, iam:ListServerCertificates, iam:GetServerCertificate, acm:ListCertificates, ssm:ListDocuments, ssm:DescribeDocumentPermission, s3:ListAllMyBuckets, s3:GetBucketLocation, cloudtrail:DescribeTrails, cloudtrail:GetTrailStatus, cloudtrail:GetEventSelectors, kinesis:ListStreams, kinesis:DescribeStreamSummary, glue:GetConnections, dynamodb:ListTables, dynamodb:DescribeTable, events:ListRules,events:DescribeRule, network-firewall:ListFirewalls, network-firewall:DescribeFirewall, backup:ListBackupPlans, backup:GetBackupPlan, backup:ListRecoveryPointsByBackupVault, codebuild:ListProjects, codebuild:BatchGetProjects, ec2:DescribeTransitGateways, ec2:DescribeTransitGatewayAttachments, rds:DescribeDBSnapshots |
| Azure | Microsoft.Logic/workflows/read, Microsoft.Security/pricings/read, Microsoft.StreamAnalytics/streamingjobs/read, Microsoft.ApiManagement/service/workspaces/read, Microsoft.Insights/activityLogAlerts/read, Microsoft.Insights/diagnosticSettings/read Microsoft.Network/bastionHosts/read, Microsoft.Cdn/profiles/endpoints/read, Microsoft.Cdn/profiles/read, Microsoft.DataProtection/backupVaults/read, Microsoft.DataProtection/backupVaults/backupPolicies/read Microsoft.Cdn/profiles/read, Microsoft.KeyVault/managedHSMs/read, Microsoft.Authorization/policyAssignments/read, Microsoft.RecoveryServices/Vaults/read, Microsoft.RecoveryServices/Vaults/backupPolicies/read Microsoft.SignalRService/SignalR/read, Microsoft.SignalRService/WebPubSub/read Microsoft.Resources/subscriptions/read |
| GCP | agentregistry.agents.list |
Resources
- TotalCloud™ – The Risk-minded CNAPP. Learn more about TotalCloud CNAPP.
- Online Help for TotalCloud, Connectors, TotalCloud API User Guide
- How-to Training Videos
- If you have questions, please contact your TAM or Qualys Technical Support.